CVEasy AI · Exposure Chart
Both exploited flaws were in attacker hands before anyone disclosed them
Between October 14 and October 28, 2026, six CVEs in our daily intel were specific enough to chart, from BeyondTrust, Ivanti, PHP, Node.js, and the eMudhra certificate authority. Two carry reports of active exploitation, and in both cases the exploitation started before the public advisory. Four have a CVSS 4.0 score and get a bar; the other two appear in a line under the chart.
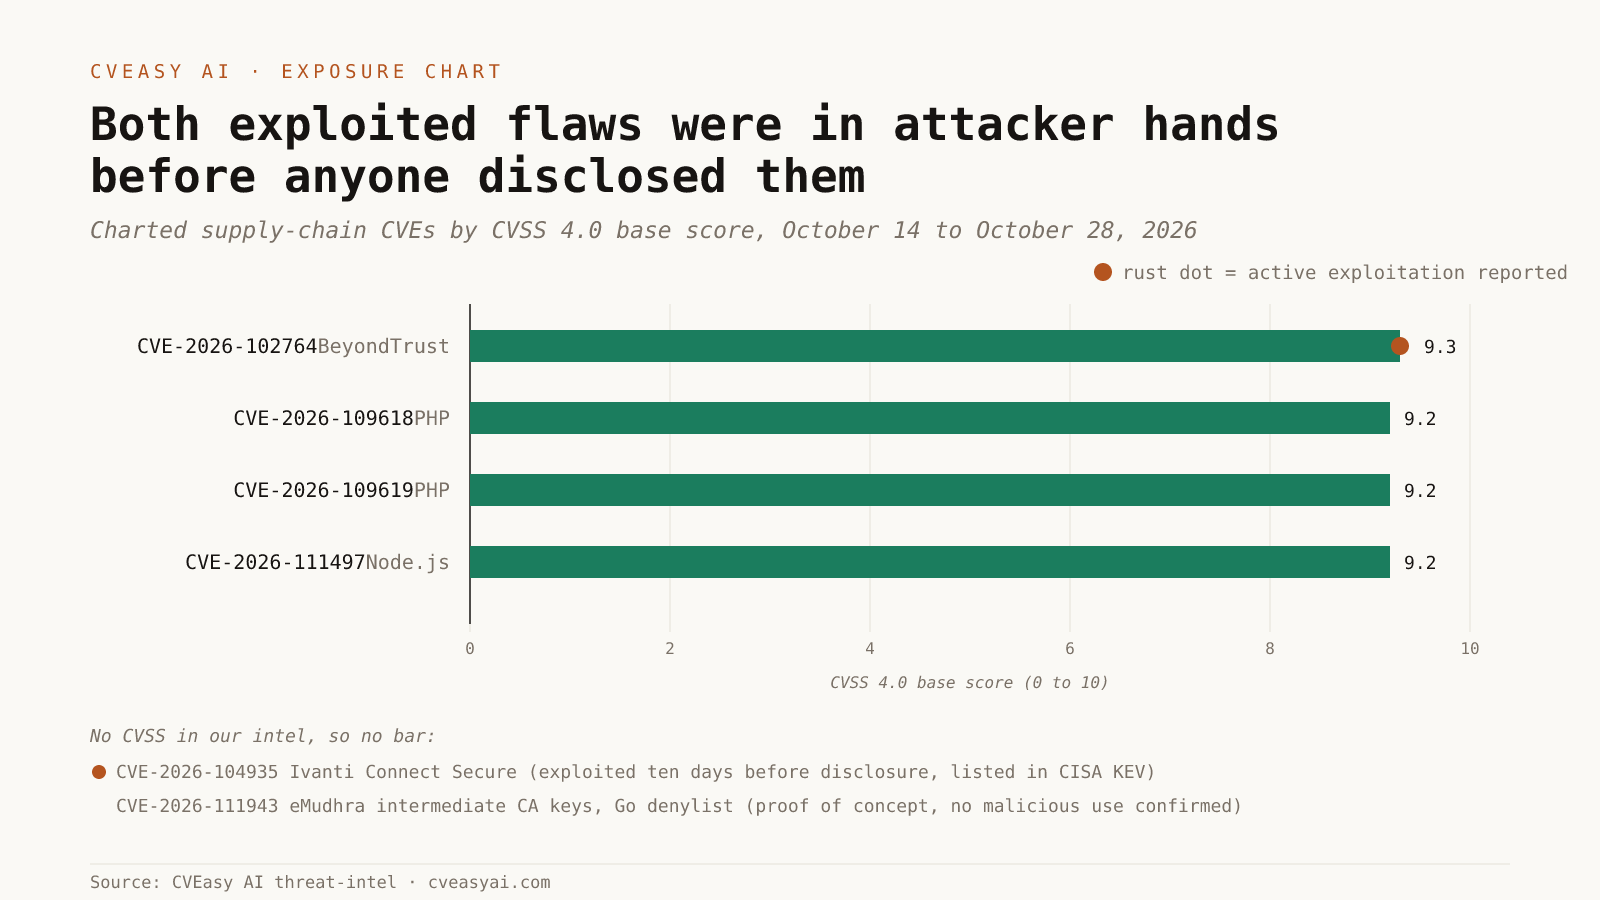
BeyondTrust Remote Support (CVE-2026-102764) tops the chart at 9.3 under CVSS 4.0 in BeyondTrust's own advisory; NIST NVD scores it 9.8 under CVSS 3.1. Mandiant attributes exploitation to the China-nexus group ARMORY CASTLE starting around August 29, 2026, and BeyondTrust disclosed it on October 15. CISA added it to KEV on October 16. Ivanti Connect Secure (CVE-2026-104935) has no score in our intel, yet Volexity observed exploitation from October 3, ten days before disclosure, and Ivanti has patched only two of the three chained flaws. The PHP2Shell pair (CVE-2026-109618 and CVE-2026-109619) and the Node.js Brotli decoder flaw (CVE-2026-111497) each score 9.2. Public PHP exploit code is circulating but unverified, and Node.js has no public proof of concept for any of its 10 October fixes.
CVSS puts these flaws within a tenth of a point of each other and gives Ivanti no number at all, so it cannot set your patch order. Exploitation status can. We would patch self-hosted BeyondTrust appliances to advisory BT26-05 and apply the Ivanti fixes first, then hunt for signs of earlier compromise, since attackers in the BeyondTrust intrusions deployed webshells and harvested credentials during roughly seven weeks of undetected access. PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 and the October 21 Node.js release come next, with PHP first because exploit code is already public.
Data: the free signed CVEasy threat-intel bundle, published weekly. Cite as "per CVEasy AI threat-intel data".
Daily exposure intel: follow CVEasy AI on LinkedIn · Weekly digest: This Week in Exposure.