CVEasy AI · Exposure Chart
The perimeter appliances were the target this fortnight
Between September 16 and 30, 2026, every supply-chain CVE serious enough to chart was already being exploited. Seven made the cut, ranked by CVSS base score, and four of the seven are the network appliances that sit at the edge of corporate networks. Cisco, F5, Check Point, and Citrix all shipped emergency fixes for flaws attackers were using before the patch landed.
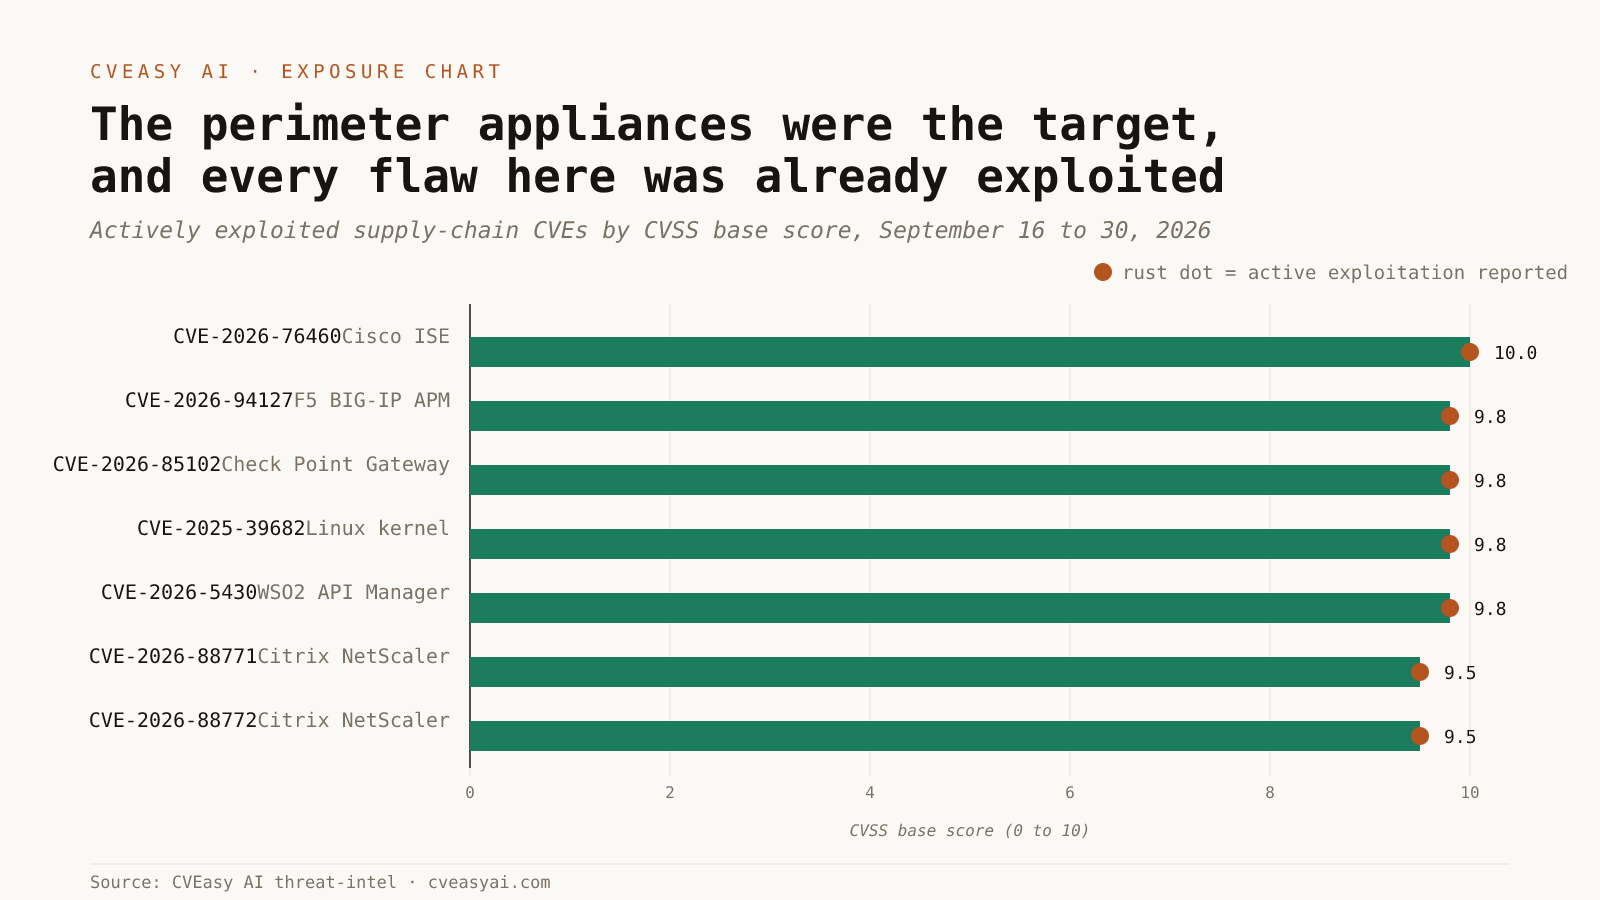
The chart reads as one solid column of green with a rust dot on every bar, which is the finding. There was no gap this fortnight between a flaw rated critical and a flaw under attack. CVE-2026-76460 in Cisco Identity Services Engine carries a perfect 10.0 and let an unauthenticated request bypass authentication entirely. CVE-2026-94127 in F5 BIG-IP APM and CVE-2026-85102 in Check Point Security Gateway both sit at 9.8, both pre-auth remote code execution, both confirmed exploited in the wild. Citrix NetScaler added two more at 9.5, CVE-2026-88771 and CVE-2026-88772, exploited before the September 27 fix existed.
The practical read is that the devices bought to guard the perimeter were the fastest way through it. Access managers, VPN gateways, and email gateways concentrate credentials and traffic, so a single pre-auth flaw in one of them is worth more to an attacker than a dozen bugs on an internal host. When a vendor advisory for one of these boxes says exploitation is already happening, the patch window is measured in hours rather than a maintenance cycle. Treat an edge appliance CVE with confirmed exploitation as an incident, not a ticket.
Data: the free signed CVEasy threat-intel bundle, published weekly. Cite as "per CVEasy AI threat-intel data".
Daily exposure intel: follow CVEasy AI on LinkedIn · Weekly digest: This Week in Exposure.